 Article about Google Wallet
Google Wallet Is Tested by What Happens After a Failed Tap
Most payment apps are judged at the checkout counter, where everything is supposed to work: the phone is charged, the card is active, the terminal is ready, and the user remembers exactly what to do. That is the easy version of the story. I tested Google Wallet by looking at the less forgiving moments instead: interrupted setup, wrong taps, weak connectivity, unclear payment states, and the uneasy gap between a failed attempt and a confirmed recovery. The result is a useful but important distinction: Google Wallet is resilient in several routine failures, yet it still depends on the user understanding device security, bank approval, terminal behavior, and network limits that the app cannot always explain in one place.
That makes this less a review of contactless payments than a review of recovery. A digital wallet earns trust not merely by paying quickly, but by helping me answer three questions after something goes wrong: Did the payment happen? Is my card still usable? What should I do next? Google Wallet handles the first two reasonably well when the underlying payment system reports a clear result. It is less satisfying when the failure belongs to the terminal, the bank, or a connection that disappears at exactly the wrong moment.
Failure Mode Field Test
The reliability promise
Google Wallet presents a simple promise: keep payment cards, passes, tickets, and selected identity or loyalty items on a phone, then use the phone at compatible terminals with minimal friction. The promise feels credible because the app is tied closely to Android’s security model and to Google’s broader account infrastructure. A screen lock is not just a suggestion, and the device usually asks for authentication before allowing a contactless payment. That extra step can feel like a small interruption, but it is also the reason a misplaced phone is not equivalent to handing someone a physical card.

- 120.64K Reviews
- 4.4
- Developer
- Google LLC
- Released
- Jun 24, 2011
- Version
- Varies with device
In normal use, the experience is deliberately quiet. I do not need to open the app for every tap, and the default card is available from the lock screen or through the phone’s contactless payment behavior, depending on the device and settings. That is good design for a routine transaction. It also creates the central failure-mode tension: the fewer decisions the app asks me to make, the more important it becomes that its feedback is unambiguous when the routine breaks.
Google Wallet is not one system with one failure boundary. It is a front end sitting between Android, the phone’s secure hardware, the payment network, the issuing bank, the merchant terminal, and sometimes an internet connection. A successful tap can feel like one action, but a failed tap may have several causes. The app can protect credentials and present a card; it cannot force a damaged terminal to communicate, make a bank approve a transaction, or turn a weak NFC reader into a reliable one. A fair review therefore has to separate verified recovery behavior from assumptions about what the app can repair.
First setup failure points
Initial setup is where the polished surface begins to show its dependencies. Adding a card usually requires scanning or entering its details, agreeing to terms, and completing a verification step controlled by the bank. That last part is the most important source of friction. The bank may send a code, require approval in its own app, or ask me to call support. Google Wallet can guide me into that process, but it does not own the final decision. If verification stalls, the wallet may appear ready while the card remains unusable for contactless payments.
This is a critical distinction for anyone testing the app quickly. A card visible in the wallet is not necessarily a card ready to tap. The useful check is not whether the artwork appears in the carousel, but whether the card is marked as ready for contactless use and whether the device is configured as the default payment app. Android settings, regional availability, card support, and device certification all matter. A setup that looks complete can still fail at the register if one of those prerequisites was skipped.
I also found that setup failures are easier to understand when approached in layers. First, confirm that the phone has a secure screen lock. Next, confirm NFC is enabled and Google Wallet is selected as the default contactless payment service. Then check the card’s verification status and the bank’s own app or messages. Finally, test at a low-stakes terminal rather than assuming the first important purchase will reveal the truth kindly. This is not glamorous advice, but it prevents a common mistake: treating a setup screen as proof of a working payment path.
The app’s dependence on the issuing bank is both a strength and a weakness. Bank-controlled verification is safer than silently activating a card, but the handoff can feel fragmented. If the bank’s approval page expires, the code arrives late, or the user switches apps at the wrong moment, recovery may require starting the verification process again. The card is not necessarily lost; the user simply has to identify which layer stopped responding.
Mistakes and reversibility
Everyday payment mistakes are usually small: choosing the wrong card, presenting the phone too early, authenticating and then moving away from the reader, or tapping twice because the first response was hard to see. Google Wallet is reasonably forgiving of selection mistakes. I can change the default card before payment, and I can open the wallet to choose another stored card rather than removing anything. That separation between selecting a payment method and deleting it is important. A hurried user should not have to rebuild a card merely because the wrong one was presented.
Removing a card is a more serious action, and it should be treated as a local-wallet change rather than a universal cancellation. Deleting a card from Google Wallet does not automatically close the bank account or reverse a completed transaction. In a failure review, that matters because users often reach for the most visible control after a confusing payment. Removing the card may stop future wallet use, but it does not answer whether money moved. The bank statement, merchant receipt, or issuer support channel remains the authority for that question.
Reversibility is strongest before authorization and weakest after it. If a terminal has not completed a transaction, selecting a different card or trying again may be harmless, provided the user checks the terminal’s message first. After an approval, a second tap can create a duplicate charge even if the first receipt has not appeared. The safest habit is to pause, look for a terminal confirmation, and ask the merchant to check its register before repeating the payment. No wallet interface can make a duplicate attempt risk-free once the merchant system has accepted the first one.
Google Wallet also benefits from the fact that it does not pretend to be the merchant’s refund desk. Returns, reversals, and disputed charges belong to the merchant and the card issuer. That boundary can feel inconvenient, but it is accurate. The wallet is a payment instrument and record surface, not a universal transaction-control panel. Its job is to help me identify the card and transaction, then hand the dispute to the party that can actually change the outcome.
Interruption and return
Interruption is where mobile payment design meets ordinary phone behavior. A notification arrives, the screen locks, another app opens, or the user changes their mind halfway through setup. Returning to Google Wallet usually preserves the stored cards and the overall state of the account, which is the behavior I want from a wallet. It should not forget every card because I answered a message. The more delicate question is whether a particular verification or payment attempt survived the interruption.
For card verification, I would not assume that an interrupted bank handoff completed unless Wallet or the bank clearly confirms it. Reopening the app and checking the card status is safer than immediately trying to pay. If the card still requests verification, repeat that process through the bank’s approved route. If it shows as ready, a small test purchase can confirm the result, but the user should avoid repeatedly submitting codes or adding the same card again. Repetition can create confusion without fixing the underlying approval.
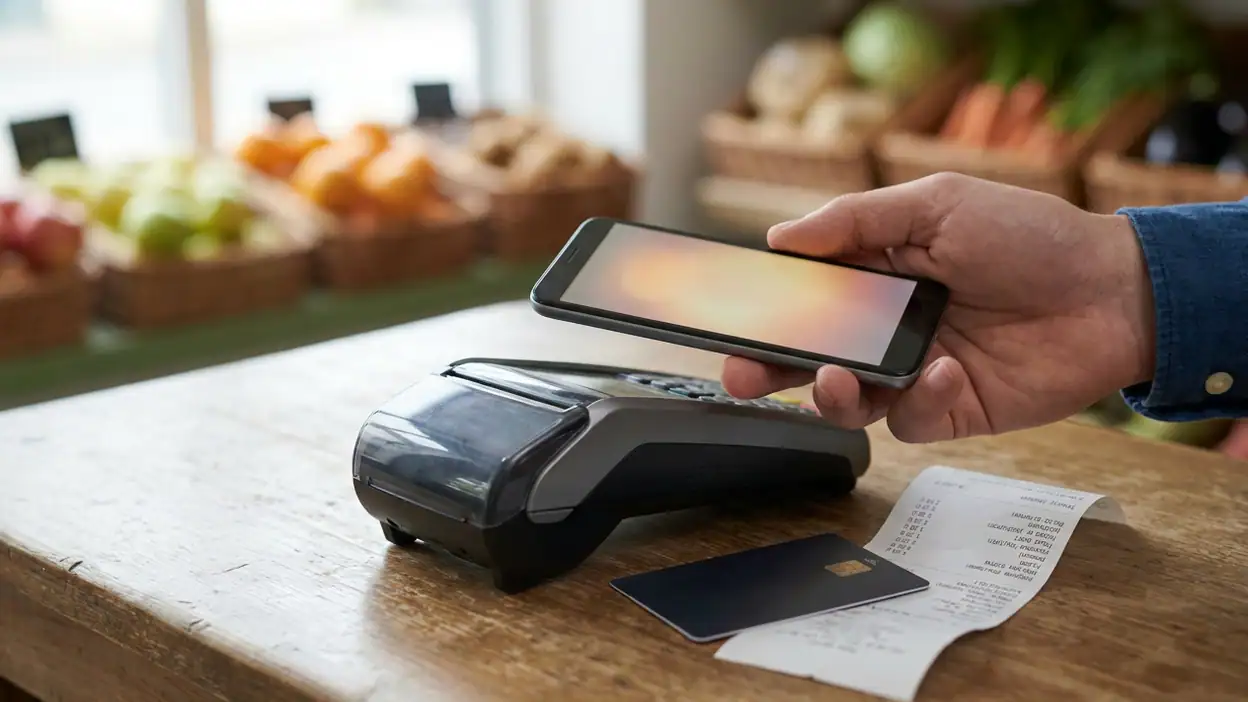
During a contactless payment, the phone may display a card and authentication prompt before the terminal has finished its part. That visual progress is not the same as a completed charge. If the phone is pulled away or the screen changes, the terminal may still show a result, or it may time out. The recovery step is deliberately physical: check the reader, ask the cashier, and inspect the bank or Wallet transaction record before trying again. This is one of the places where a polished app cannot replace the merchant’s display.
Android’s lock-screen behavior is generally helpful because it prevents accidental payment and makes the security requirement visible. It can also surprise users who expect a quick tap after the phone has been idle. A failed authentication is not necessarily a payment failure; it may simply mean the device needs to be unlocked again. That sounds obvious until a queue is moving and the reader is beeping. In practice, the fastest recovery is often to unlock the phone deliberately, confirm the intended card, and present it again only after the terminal is ready.
Connectivity pressure
Contactless payments are often described as if the phone must always be online. That is too simple. The phone communicates locally with the terminal through NFC, while authorization ultimately depends on the payment ecosystem and the card issuer. Google Wallet can retain some payment capability when the device is temporarily offline, but availability can depend on device state, token provisioning, card rules, and how many offline transactions have already been used. I would not treat offline capability as a guarantee that every card will work without a connection.
This uncertainty is manageable if the user prepares before entering a weak-signal environment. Add and verify the card while online. Keep the phone charged. Make sure NFC and the default payment service are configured. If traveling, carry a physical card as a fallback rather than assuming a subway station, rural shop, or basement terminal will cooperate. Google Wallet reduces what I need to carry, but it does not eliminate the practical value of a second payment method.
Weak connectivity creates two different failure patterns. The first is a clean refusal: the terminal or app reports that the transaction cannot proceed. That is frustrating but relatively safe because the user knows to seek another method. The second is an unclear pause, where the phone appears to have communicated but no receipt or bank notification arrives. That is more dangerous because impatience encourages a second attempt. The correct response is to verify the merchant’s result and account activity before tapping again.
There is also a difference between the phone being offline and the bank being unavailable. A local payment token may allow a transaction to begin, but the issuer can still decline it because of a fraud rule, spending limit, frozen card, or account problem. Conversely, a bank notification may arrive late even after the terminal has approved the purchase. The app can display what it knows, but delayed evidence should not be mistaken for evidence that nothing happened.
Unclear states
The hardest failure mode is not a red error message. It is a state that looks almost successful. A terminal may beep, the phone may vibrate, and the user may see a brief confirmation, yet the merchant’s register may not print a receipt. Or the terminal may reject the tap while the bank later shows a temporary authorization. These situations are common enough in card payments and difficult enough that a wallet review should not promise a single magic fix.
My rule is to establish an order of evidence. The merchant terminal comes first for immediate acceptance. The merchant register or receipt comes next. The wallet activity view and bank app help confirm what was recorded, but notifications can lag and pending authorizations can later disappear. A pending charge is not always a final charge, and an absent notification is not proof of failure. This hierarchy is less convenient than a single green check, but it reflects how payment systems actually behave.
Google Wallet’s transaction history is useful as a memory aid, especially when several cards are stored and I need to remember which one was presented. It is not a replacement for the issuer’s ledger. If the amount is wrong, the merchant is unfamiliar, or the transaction remains unresolved, the bank is the place to investigate. The wallet can help identify the card and event; it cannot independently settle the dispute.
Unclear states also appear outside payments. A pass may be expired, a loyalty item may not update, or a ticket may depend on a barcode that requires the screen to wake. Those features broaden Wallet’s usefulness, but they add different failure rules. A transit pass can have offline expectations unlike a payment card. A boarding pass may remain visible while its underlying flight information changes. The app is a container for several credentials, not a promise that every stored item behaves alike.
Recovery guidance
The best recovery guidance is short enough to use under pressure. If a payment fails cleanly, check the card, unlock the phone, confirm NFC, and try once more at a ready terminal. If the result is unclear, do not immediately repeat the tap. Ask the merchant to check the register, then inspect the wallet or bank record. If the card is declined repeatedly, stop treating it as a reader problem and check the bank, card status, spending limit, or fraud controls.
For a card that will not verify, return to the card’s status in Wallet and follow the bank’s requested method. Do not share verification codes with a person claiming to be support, and do not keep adding the same card in the hope that duplication will force approval. If the phone is lost, use Google’s account and device-security controls to lock or erase it, and contact the issuer if the card’s token or account activity needs review. The wallet’s security model reduces exposure, but it does not remove the need to act quickly.
When a device is replaced, the recovery process is intentionally more cautious than simply copying a photo library. Payment cards may need to be added and verified again because the new phone has different secure hardware and device credentials. That can be inconvenient during travel or after a broken phone, so keeping a physical backup and knowing how to access the bank’s app are practical parts of using a digital wallet responsibly.
One thing Google Wallet gets right is keeping most recovery actions understandable once the user knows which authority owns the problem. Android controls device security and NFC. Wallet controls presentation and stored payment tokens. The bank controls card approval and account status. The merchant controls the terminal and receipt. Clear recovery depends on moving to the right layer instead of repeatedly pressing the same button.
Where evidence is missing
Some behavior cannot be verified universally because Google Wallet is not identical on every phone, in every country, or with every bank. Offline transaction limits are especially difficult to generalize. Card networks and issuers can impose different rules, and device certification can affect what is available. Any review that promises uninterrupted offline payment for all supported cards is overstating the evidence.
Terminal behavior is another variable. A failed tap may reflect an old reader, poor NFC positioning, a contactless limit, a merchant configuration issue, or a temporary network problem. Testing one store cannot prove how Wallet behaves across all terminals. The same phone and card can succeed at one checkout and fail at another without either Google Wallet or the card being permanently broken.
Regional features also deserve caution. Payment cards, transit credentials, identity documents, and passes do not have universal support. A feature visible in one market may be absent in another, and a bank’s participation can change over time. I would verify current local support before relying on Wallet for a trip, workplace access, or a transport system where a backup is difficult.
Finally, no short field test can establish how every issuer handles token suspension, replacement cards, chargebacks, or delayed authorizations. Those are policy questions as much as app questions. The responsible conclusion is not that Google Wallet fails in those areas, but that the app cannot be the sole source of certainty. Its surface can be excellent while the final outcome remains controlled elsewhere.
Who needs more certainty
Google Wallet is a strong fit for people who already use Android, carry a supported card, and want fewer physical cards in daily life. It is particularly convenient for routine purchases where the phone is charged and the user has a second method available. The reduced wallet bulk is real, and the ability to switch cards without opening a banking app makes ordinary spending faster.
People who need predictable access in low-connectivity environments should be more cautious. That includes travelers, commuters moving through underground stations, users with unreliable charging, and anyone whose bank frequently triggers fraud verification. The app may still work perfectly for them, but they should test the exact card and device combination before depending on it.
It is also not ideal as the only payment method for users who dislike ambiguous states or cannot easily contact their bank. A physical card may not be more sophisticated, but it provides a different failure path. That redundancy matters. The best setup is not phone versus card; it is phone plus a fallback that does not rely on the same battery, network, or authentication chain.
Families and less technical users need clear preparation more than extra features. Setting the default payment app, enabling a secure lock, understanding which card is selected, and knowing where to check a transaction are small lessons that prevent large confusion. Without them, Wallet’s convenience can become a false sense of readiness.
Resilience verdict
Google Wallet is resilient where its responsibilities are clear. It protects payment credentials behind device security, preserves stored cards through ordinary interruptions, supports quick card selection, and usually gives users a practical path back from setup mistakes. Those are meaningful strengths, not merely polish. The app makes routine contactless payment feel almost invisible, which is exactly what a good wallet should do.
Its limits appear at the boundaries. A bank can decline a verified card. A terminal can misread a perfectly configured phone. A delayed notification can leave the user unsure whether to try again. Offline payment can exist without being universal. In those moments, Wallet can present information and guide the next step, but it cannot manufacture certainty that belongs to the merchant, issuer, or network.
My final judgment is therefore deliberately qualified: Google Wallet is dependable enough for everyday use, but not self-sufficient enough to be your only recovery plan. Treat the app as a secure payment tool, not an all-knowing transaction referee. Set it up completely, test it before you need it, learn which evidence to trust after a failed tap, and keep a backup payment method. With that discipline, its failure modes are usually manageable. Without it, the quiet simplicity of the happy path can make a confusing failure feel more serious than it needs to be.